Exploitation Techniques in Red Teaming - Nexus ESTIN Security Workshop
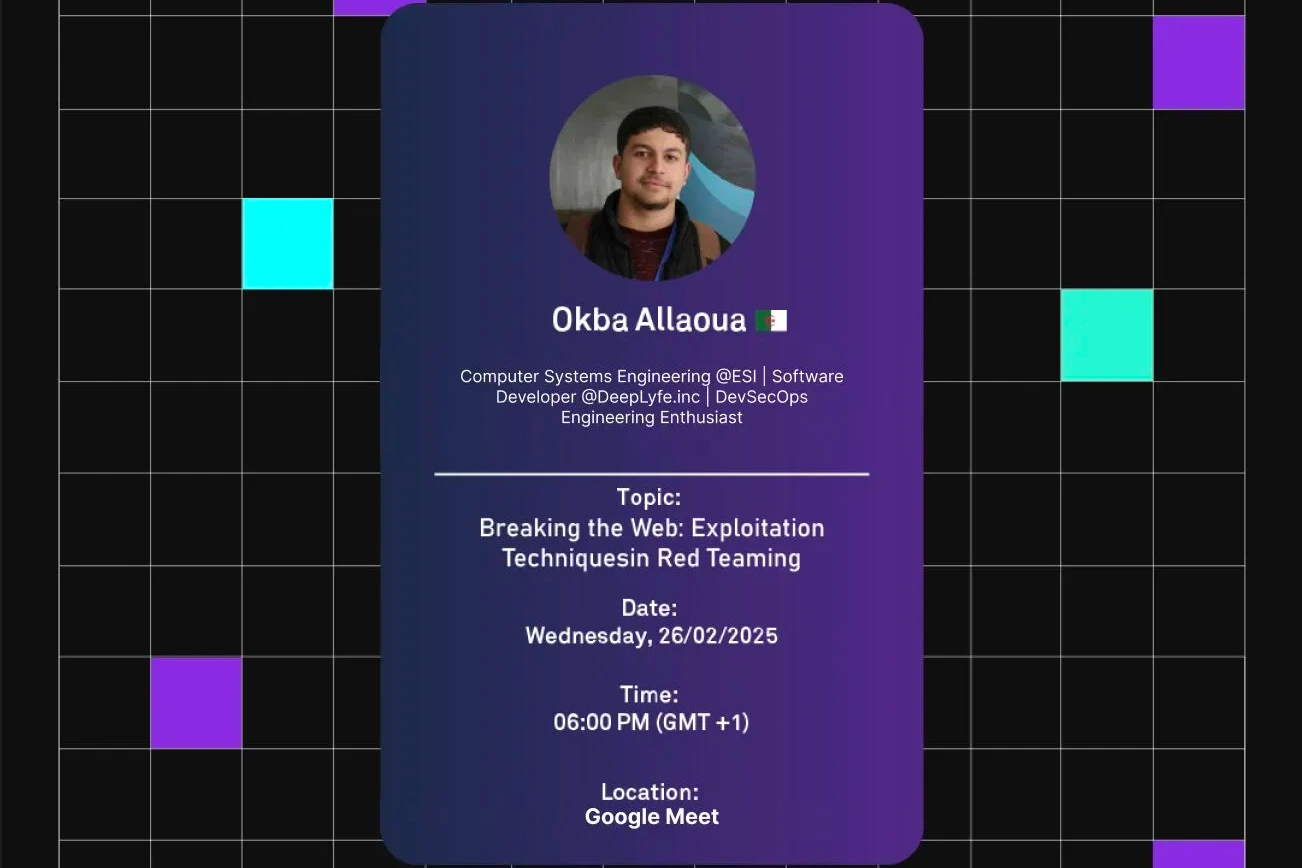
At Nexus ESTIN, I had the opportunity to dive deep into the fascinating world of red teaming with a workshop dedicated to exploitation techniques. The session provided participants with a structured overview of how attackers identify, analyze, and exploit vulnerabilities during simulated engagements.
Workshop Overview
Red teaming goes beyond basic penetration testing—it simulates real-world adversaries to help organizations understand their security posture from an attacker’s perspective. This workshop focused on the practical techniques red teamers use.
Core Topics Covered
Web Exploits (General)
- Common web attack surfaces and misconfigurations
- Input validation issues and their impact
- Authentication and authorization pitfalls
- Real-world examples mapped to defensive takeaways
Hands-On Labs
Participants gained practical experience through:
Lab 1: Broken Time-Based UUIDs
- Predictable identifier generation
- Enumerating and accessing unintended records
Lab 2: Firebase Misconfiguration
- Insecure rules and overexposed data
- Reading/writing data beyond intended scope
Lab 3: Unsanitized Input → RCE
- Dangerous input handling patterns
- How unsafe inputs can escalate to remote code execution
Ethical Considerations
We emphasized the ethical applications throughout:
- Authorization: Always have written permission
- Scope Adherence: Stay within defined boundaries
- Responsible Disclosure: Report vulnerabilities properly
- Legal Implications: Understanding laws and regulations
- Professional Ethics: Red teaming code of conduct
Tools & Frameworks
Participants learned to use industry-standard tools:
Reconnaissance
- Nmap, Masscan, Shodan
- theHarvester, Recon-ng
- OSINT Framework
Exploitation
- Metasploit Framework
- Custom exploits in Python
- SQLmap, Burp Suite, FirePwnTool
Post-Exploitation
- Empire, Covenant
- Mimikatz, BloodHound
- PowerShell Empire
C2 Frameworks
- Cobalt Strike concepts
- Sliver, Havoc C2
- Custom C2 development
Real-World Scenarios
By blending theoretical foundations with hands-on labs, attendees gained a clearer understanding of:
- How red teamers operate in enterprise environments
- The attacker’s methodology and mindset
- How these insights contribute to strengthening an organization’s security posture
- The difference between red teaming and penetration testing
Learning Outcomes
Participants left with:
- Understanding of complete attack lifecycle
- Practical exploitation techniques
- Knowledge of privilege escalation methods
- Post-exploitation tradecraft
- Defensive implications of offensive techniques
- Career paths in offensive security
Impact on Defense
Understanding offensive techniques makes you a better defender:
- Think Like an Attacker: Anticipate attack vectors
- Prioritize Defenses: Focus on high-impact areas
- Validate Controls: Test security measures effectively
- Incident Response: Better detection and response
Event Details:
- Place: Nexus ESTIN - Online
- Date: February 26, 2025
- Format: Workshop with hands-on labs
- Attendees: 35+ security enthusiasts
- Lab Environment: Isolated vulnerable infrastructure
- Duration: Half-day intensive training
This workshop demonstrated how understanding offensive techniques is crucial for building robust defensive strategies!
Resources Shared
- Red team methodology frameworks
- Privilege escalation checklists
- Post-exploitation playbooks
- Tool repositories and documentation
- Further learning paths in offensive security